Is Your Data Safe? Cybercrime Risks in 2025 & Beyond

Cybercrime no longer moves at human speed. In 2026, attackers are using generative and agentic AI to write convincing phishing lures in minutes, clone executives’ voices for help-desk scams, and probe enterprise networks faster than most security teams can respond. That shift is the single biggest force behind current cyber security market growth, and it is rewriting how vendors, buyers, and investors think about defense.
The numbers back this up. Global spending on protection is climbing in step with the threat: the cyber security market is being pulled upward by the same pressures that used to be background noise cloud migration, IoT sprawl, and regulatory tightening but AI has moved from a minor driver to the dominant one. What follows is a look at where the money and the risk are actually moving right now, drawn from the last two quarters of vendor earnings, product launches, and breach research.
The AI Threat Escalation Is Now Showing Up in the Numbers
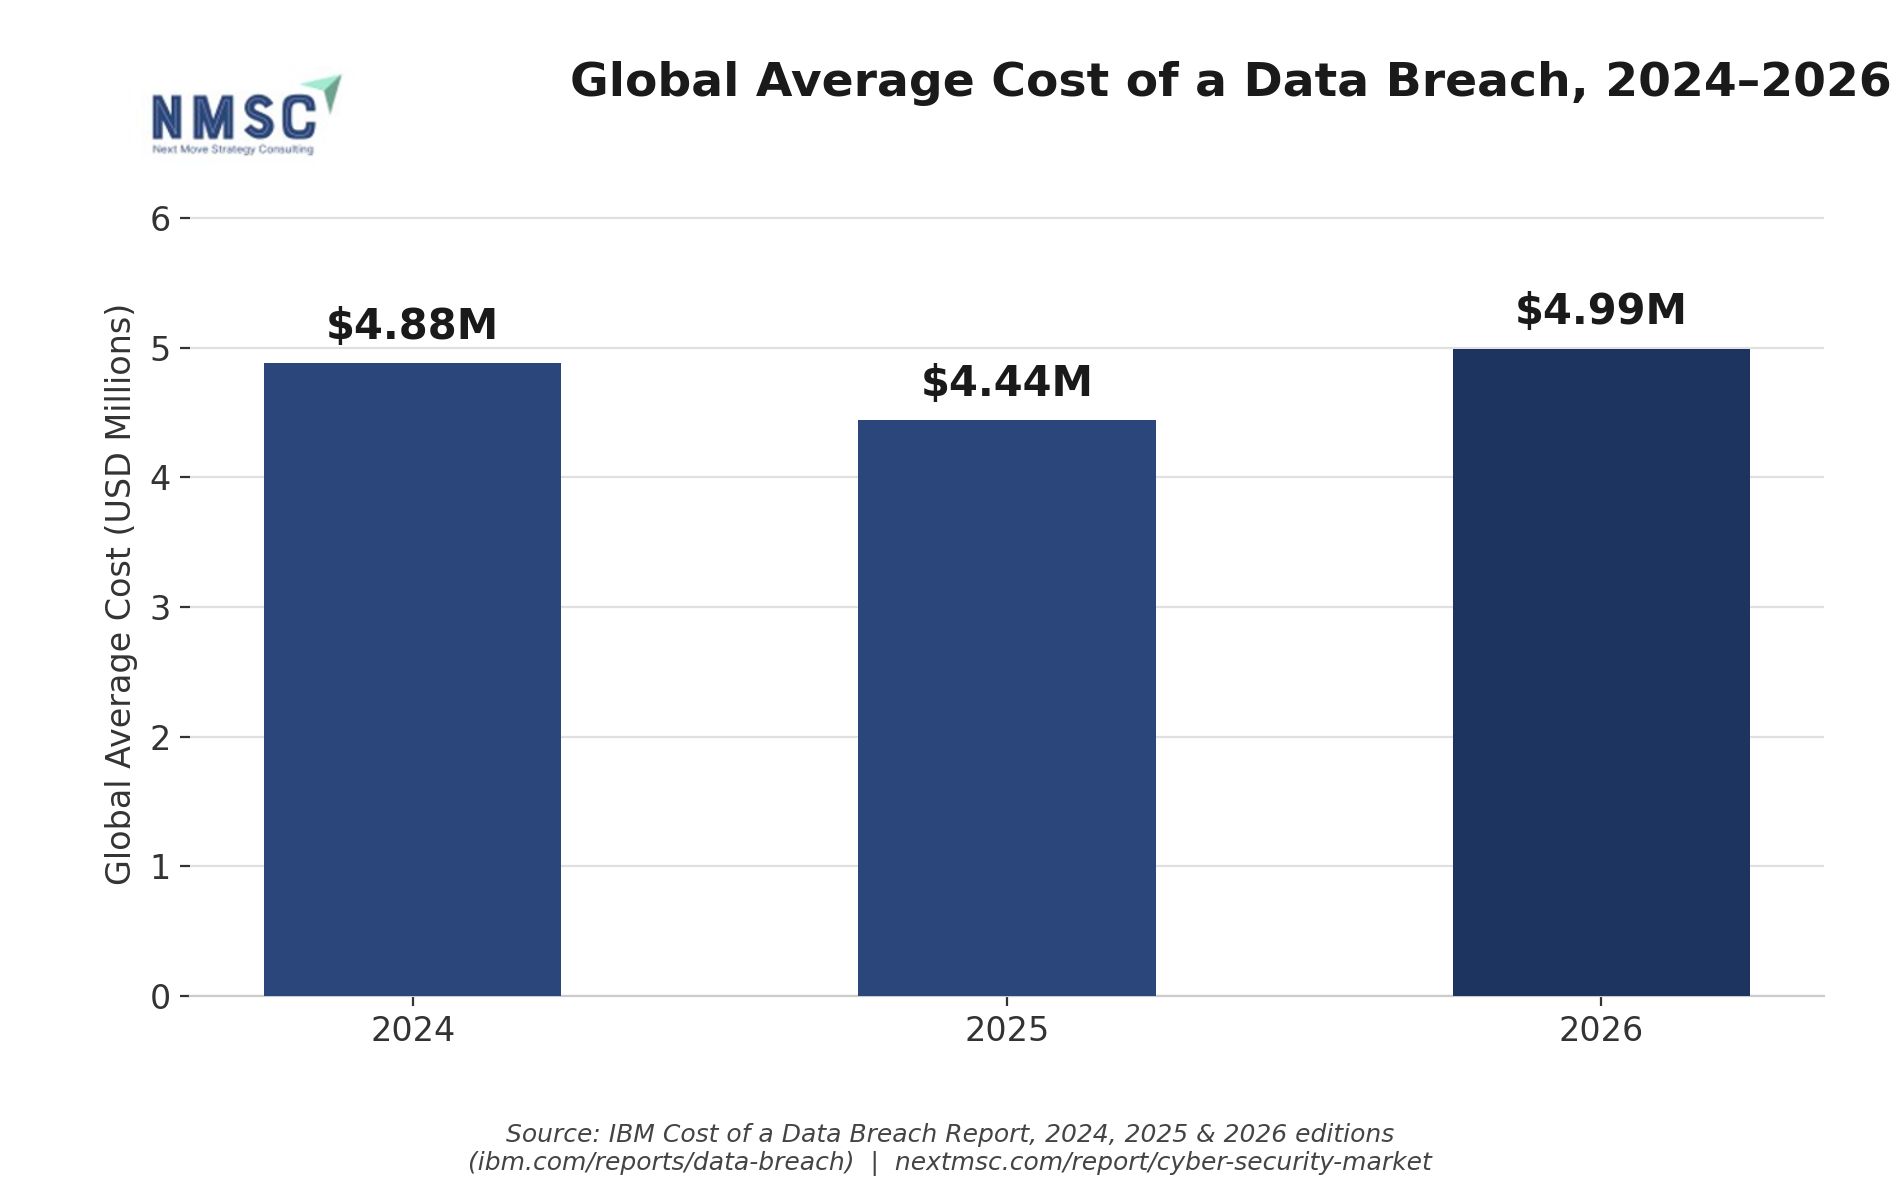
For years, the industry could point to steadily improving breach economics as proof that defensive AI was winning. That streak broke in 2026. The global average cost of a data breach hit a record $4.99 million, a 12% jump from the year before, driven mainly by higher detection, escalation, and lost-business costs. It's a sharp reversal from 2025, when faster AI-assisted containment had actually pushed the average down to $4.44 million.
The reason for the reversal is straightforward: attackers adopted AI faster than most defenders adopted the governance to control it. One in four malicious breaches studied were AI-enabled, a 56% jump year over year, and those incidents carried an average cost of roughly $6 million about $1 million more than the overall average. Among organizations that suffered an AI-related incident, the vast majority had no meaningful access controls on their AI systems at the time. That gap, more than any single exploit, is what's driving enterprise security budgets right now.
-
Global average breach cost: $4.99M in 2026, up 12% year over year a new record
-
AI-enabled breaches now average roughly $6M, about 20% above the overall average
-
AI-driven attacks rose 56% year over year and account for roughly one in four malicious breaches
Industry Leader Moves: The Race to Govern AI Agents
Zoom out across the market's largest vendors and one theme dominates every recent product launch and acquisition: securing non-human identity. As enterprises hand more work to autonomous AI agents, those agents become privileged users in their own right and most identity systems were never built to track them.
|
Company |
Move |
Date |
Scale / Value |
Strategic Focus |
|
Palo Alto Networks |
Completed acquisition of CyberArk |
Feb 2026 |
$25B |
Identity security platform |
|
Palo Alto Networks |
Acquired Console, an AI-native IT automation platform |
Sep 2026 |
~$500M |
Agentic operations |
|
CrowdStrike |
Acquired SGNL; launched Continuous Identity for AI Agents |
Jan / Jun 2026 |
Undisclosed |
Non-human identity governance |
|
Microsoft |
Agent 365 reached general availability (Microsoft 365 E7 Frontier Suite) |
May 2026 |
$15/user/mo (Agent 365) |
AI agent control plane |
|
Fortinet |
Partnership with Intel on custom Security Processor 6 (SP6) |
Jul 2026 |
Undisclosed |
AI-era hardware acceleration |
|
Cisco (Splunk) |
Launched Cisco AI POD for Splunk with NVIDIA, on-prem/air-gapped |
Sep 2026 |
Undisclosed |
Agentic security operations |
|
Zscaler |
Acquired Symmetry Systems to build an AI Access Graph |
May 2026 |
$175M |
AI agent access governance |
|
IBM |
watsonx Orchestrate evolved into an “Agentic Control Plane” |
May 2026 |
N/A |
Multi-agent governance |
Palo Alto Networks has moved the most aggressively on cost. Its $25 billion acquisition of CyberArk closed in February, establishing identity security as a core platform pillar, and the company followed it with a run of smaller, faster deals Koi for agentic endpoint security in April, Portkey for AI gateway control in May, and Console, an AI-native IT automation platform, for roughly $500 million in September. CrowdStrike has taken a similar path from the identity side, turning its January acquisition of SGNL into Continuous Identity for AI Agents and, more recently, an Agentic Identity Provider that registers every AI agent as a cryptographically verifiable, non-spoofable identity.
Microsoft and Cisco are approaching the same problem from the operations side. Microsoft's Agent 365, generally available since May as part of its Microsoft 365 E7 Frontier Suite, acts as a control plane for discovering and governing agents across Microsoft's own tools as well as third-party and locally run agents. Cisco, building on its Splunk integration, used its mid-September .conf26 event to bring self-managed Splunk AI on-premises and to air-gapped environments for the first time, alongside a new multi-year co-development agreement with AWS aimed squarely at AI-driven attacks. Fortinet, meanwhile, is leaning on its hardware advantage: a July partnership with Intel on a custom security processor, and a second-quarter revenue jump of 26% that the company attributes largely to AI-driven demand for network and data-center protection.
Zscaler and IBM round out the picture from two different angles. Zscaler spent roughly $175 million in May on Symmetry Systems to build an “AI Access Graph” mapping how identities, applications, and data connect technology it has since folded into a broader AI Broker and Agent Registry for controlling agent-to-agent traffic. IBM, for its part, is both selling the fix and measuring the problem: its watsonx Orchestrate platform is evolving into what the company calls an “Agentic Control Plane” for governing thousands of agents at once, while its own annual breach research remains the industry's most-cited evidence of why that governance gap matters.
-
Palo Alto Networks closed its $25B CyberArk acquisition in February and made at least three further AI-security deals in 2026
-
CrowdStrike, Microsoft, Cisco, Zscaler, and IBM have each shipped a dedicated “agent governance” product or platform update since January 2026
-
Fortinet posted 26% revenue growth in Q2 2026 and is partnering with Intel on purpose-built security hardware for AI workloads
Where the Investment Is Going Next
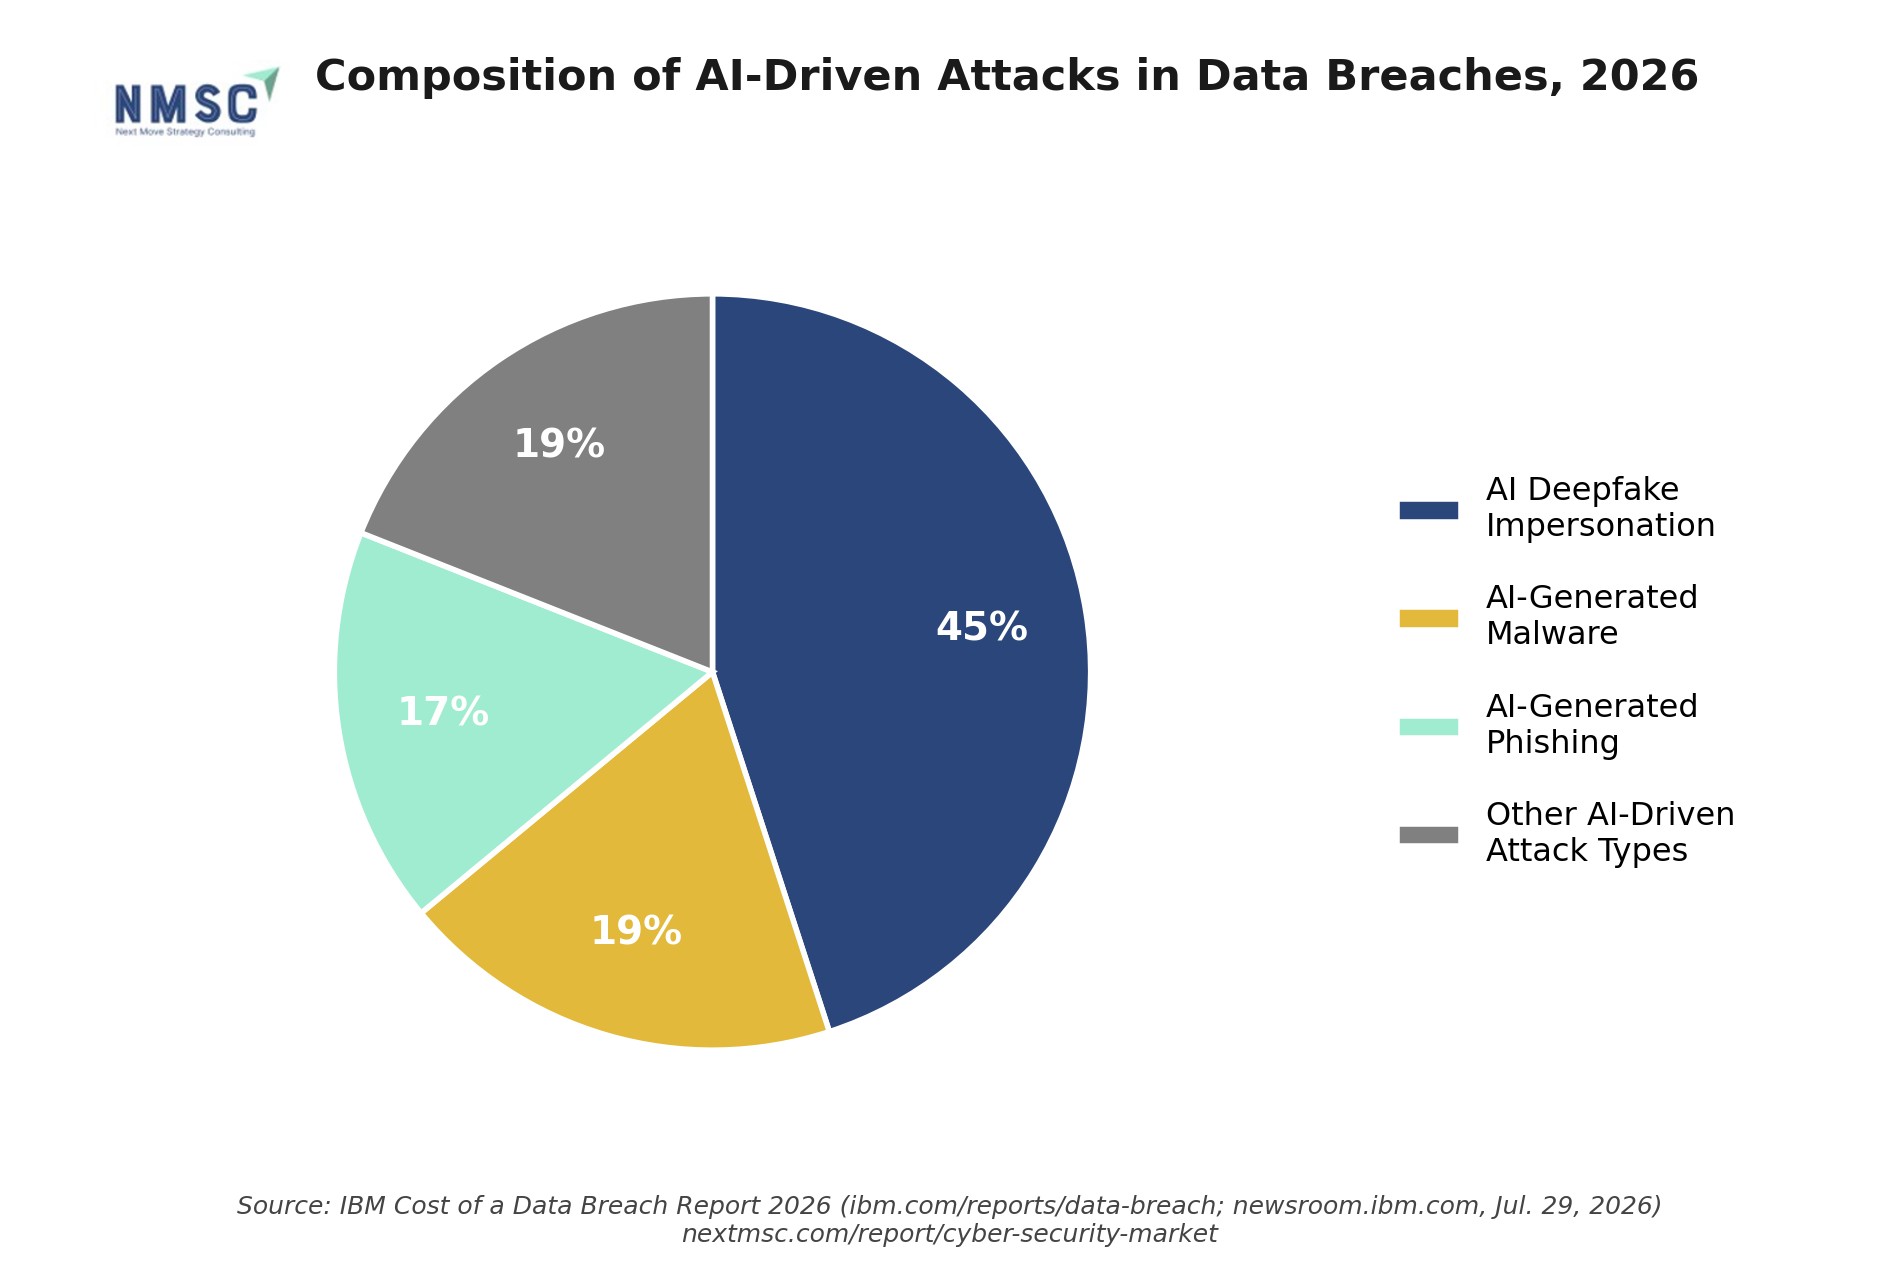
The shape of AI-driven attacks helps explain where defensive spending is concentrating. Deepfake impersonation fraudulent video or voice used to trick employees, most often in help-desk or executive-approval scams now accounts for the largest share of AI-driven attacks, well ahead of AI-generated malware and AI-written phishing. That pattern is a big part of why identity verification, rather than traditional perimeter defense, has become the industry's most active battleground, and it's fueling parallel growth in AI-based security operations, where vendors are building AI systems specifically to investigate and respond to AI-driven incidents at machine speed.
Two other trends are compounding the shift. Adoption of zero trust architectures continues to accelerate as a direct response to agent sprawl, since “verify every request” is a more workable model for machine identities than perimeter-based trust ever was. And cloud security posture management tools are being pulled into the same AI-governance conversation, since misconfigured cloud permissions are one of the easiest ways an autonomous agent or an attacker impersonating one can gain excessive access. On the network and application side, vendors are also converging previously separate tools into single platforms: web application and API protection, for instance, is increasingly sold as one continuous discover-scan-protect-monitor loop rather than a stack of point products, a shift visible in platforms such as Indusface's AppTrana.
Fortinet's own commentary is a useful signal of scale here: the company estimates the AI security segment specifically as distinct from cybersecurity overall could reach $172 billion by 2029, growing more than four times faster than the broader market. Regulated, high-value sectors are absorbing a disproportionate share of the risk in the meantime: financial services and energy together account for well over half of AI-driven attacks tracked in 2026, and operational technology security spending is rising accordingly as critical-infrastructure operators come under the same pressure.
-
Deepfake impersonation is the single largest category of AI-driven attack, ahead of AI-generated malware and phishing
-
Zero trust and cloud security posture management are being pulled into the AI-governance conversation as agent sprawl grows
-
Financial services and energy organizations are absorbing a disproportionate share of AI-driven attack activity in 2026
Cyber Security Market Outlook
|
Parameter |
Detail |
|
Market Size (2021, base year) |
USD 197.4 Billion |
|
Market Size (2022) |
USD 221.72 Billion |
|
Revenue Forecast (2030) |
USD 657.02 Billion |
|
CAGR (2022–2030) |
12.8% |
|
Largest Regional Share |
North America |
|
Companies Profiled |
20 |
|
Countries Covered |
26 |
|
Key Security Domains Tracked |
Perimeter & Network, Endpoint & Mobile, Data & Application, Identity & Access Management, Intelligence & Analytics, Emerging Tech |
Against this backdrop, the broader cyber security market's trajectory looks less like a forecast and more like a description of what's already underway. Growth is being propelled by the same two forces that have driven it for several years rising phishing and malware activity, and the security demands created by IoT, AI, and bring-your-own-device adoption across e-commerce and enterprise platforms alike with North America continuing to hold the largest regional share on the strength of its cloud adoption and government and healthcare spending.
For organizations trying to size their own investment against that backdrop, the practical questions have shifted. It's no longer just “how much firewall or antivirus coverage do we need,” but “do we know every AI agent operating in our environment, and can we prove who or what is acting on our data at any given moment.” Download Free Sample
What This Means for Security Leaders
The cyber security market of 2026 is being reshaped less by new categories of threat than by a new category of actor: the autonomous AI agent, on both sides of the fight. Vendors that can prove they know which agents are running, what they're allowed to touch, and how fast they can be stopped when something goes wrong are pulling ahead of the pack and buyers are increasingly making purchasing decisions on exactly that basis. For most organizations, the near-term priority isn't necessarily a bigger security budget; it's closing the same access-control gap that left the vast majority of this year's AI-related breaches without adequate access controls in place.
About the Author
 Sanyukta Deb
— Sanyukta Deb is Digital Marketing Team Lead at Next Move Strategy Consulting, where she has led content strategy and technical SEO for the firm's B2B market research publications for over 2 years. Her editorial process translates NextMSC's primary and secondary research — spanning technology, industrial, and consumer sectors — into commercial narratives, backed by search-intent, keyword, and competitive analysis. She brings 5 years of overall experience in digital marketing and content strategy.
About the Reviewer
 Debashree Dey
— Debashree Dey is Assistant Manager at Next Move Strategy Consulting, where she supports cross-vertical market content and communications across diverse industries for 6 years. Her professional background includes senior content writing, communications, and published manuscript authorship, with experience developing audience-focused business narratives and maintaining clear, consistent messaging. Her role supports research-led content development and editorial quality across NextMSC publications.














Add Comment