How Businesses Can Improve Ethical Standards for Sustainable Profitability

Governance, risk, and compliance used to mean a policy binder, an annual audit, and a set of approval workflows. That model is running out of road. AI agents are now embedded in everyday business processes, regulatory obligations are multiplying across jurisdictions, and boards want proof that controls actually work not a spreadsheet showing someone checked a box. That shift is why the governance, risk, and compliance (GRC) platform market is moving fast toward connected systems that can map obligations, automate controls, and give executives a current view of enterprise exposure.
Why the GRC Platform Market Is Accelerating
GRC Platform Market Snapshot: Size, Forecast, and CAGR
|
Metric |
Value |
|
Market Size (2024) |
USD 40.55 Billion |
|
Market Size (2025) |
USD 45.30 Billion |
|
Revenue Forecast (2030) |
USD 78.89 Billion |
|
CAGR (2025–2030) |
11.73% |
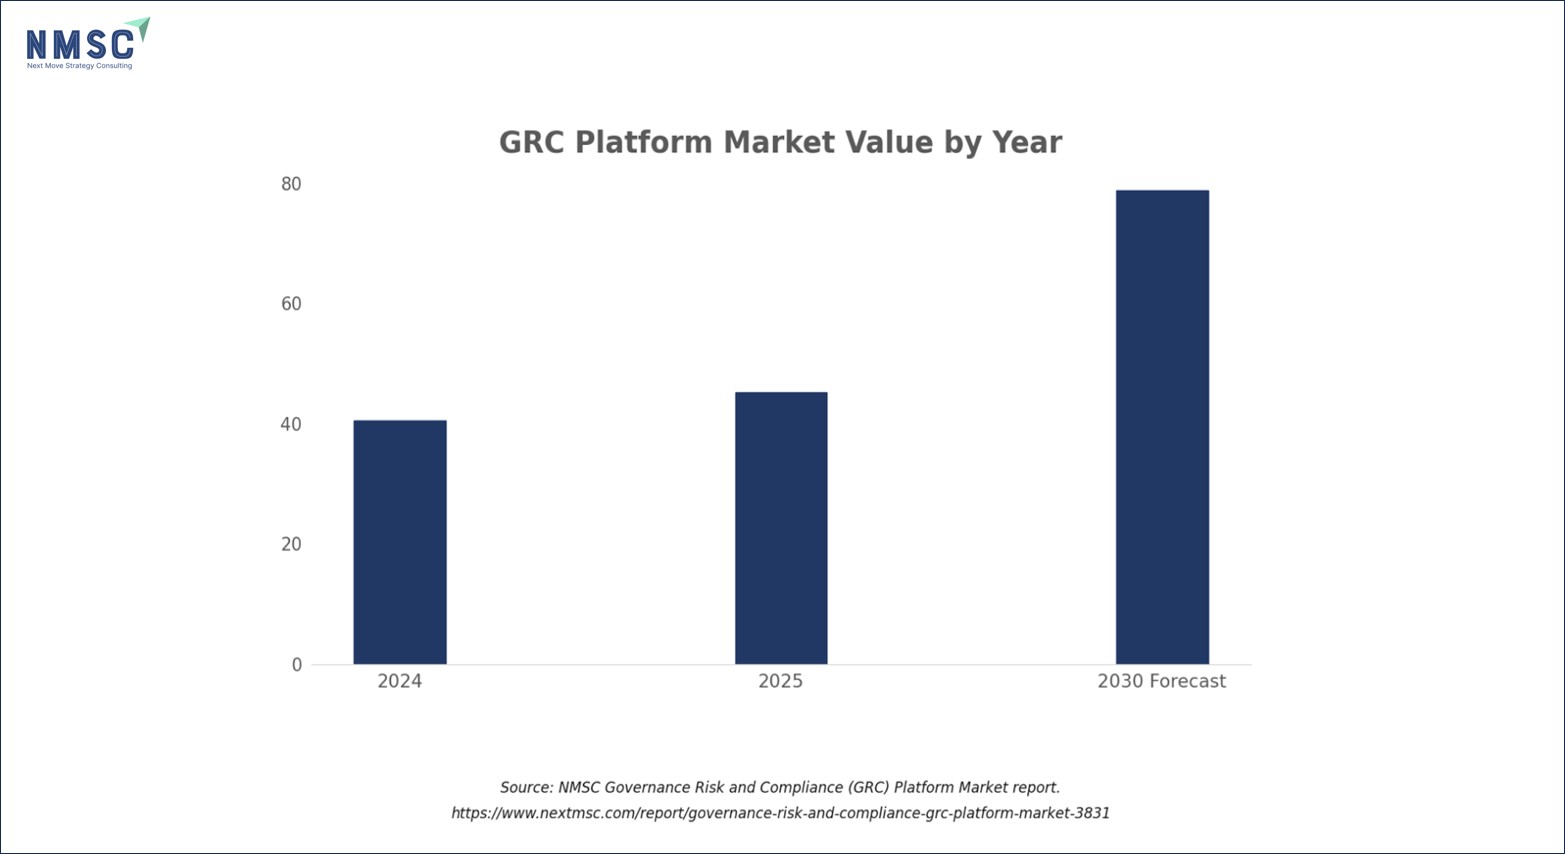
According to NMSC's analysis, the market is set to nearly double by 2030. The growth isn't evenly spread: on component, software still leads, with services layered in as programs mature; on deployment, cloud-native SaaS is gaining share fastest, though regulated industries still favor on-premises and hybrid setups for data control; and among solution types, compliance management and enterprise risk management remain the anchors, with third-party risk management and ESG reporting as the fastest-growing niches. North America remains the dominant region, per NMSC, with Asia-Pacific growing fastest.
AI Governance Has Become a Core GRC Workload
The clearest driver of platform investment right now is that AI has expanded what governance has to cover. Enterprises no longer just govern employees and applications they need governance for models, agents, and automated decisions, which introduces a new class of non-human identity to track.
Two recent moves illustrate this. In May 2026, ServiceNow expanded its AI Control Tower to discover AI assets across more than 30 third-party integrations, monitor agent behavior at runtime, and apply risk frameworks aligned to NIST and the EU AI Act, adding real-time enforcement rather than just visibility. Around the same time, IBM described its own roadmap as a shift from periodic AI governance toward continuous AI assurance: connecting live system metrics to controls, risks, and named owners so compliance status can be verified continuously rather than checked once a quarter.
Regulation is reinforcing the same shift. The EU AI Act's Article 50 transparency obligations, covering disclosure when a person is interacting with an AI system and machine-readable marking of AI-generated content, took effect August 2, 2026, with the European Commission publishing interpretive guidelines the previous month. Non-compliance can trigger fines of up to €15 million or 3% of worldwide annual turnover, whichever is higher. Separately, in April 2026 the U.S. National Institute of Standards and Technology opened work on a dedicated AI Risk Management Framework profile for critical infrastructure, signaling that AI risk practices are becoming sector-specific rather than one-size-fits-all.
Section summary: AI governance has moved from a research topic to an operational, enforceable requirement, and GRC platforms are the systems being asked to carry that load.
Governance now extends to non-human identities AI agents and automated decisions not just employees and applications
Vendors are adding real-time enforcement, not just dashboards, to AI oversight
EU transparency rules are already in force and carry material fines; sector-specific AI risk frameworks are emerging in the US
Cyber, Compliance, and Third-Party Risk Are Converging
Recent Regulatory Signals Driving GRC Platform Adoption
|
Development |
Status / Date |
Source |
|
EU AI Act Article 50 transparency duties |
In force since Aug 2, 2026 |
European Commission |
|
EU AI Act Article 50 penalties |
Up to €15M or 3% of global turnover |
European Commission |
|
NIST AI RMF critical-infrastructure profile |
Concept note published Apr 7, 2026 |
NIST |
|
EBA Risk Assessment Report |
Published June 2026; flags frontier-AI/LLM cyber risk to banks |
European Banking Authority |
|
US bank supervision refocused on material financial risk |
Final rule published Sept 1, 2026; effective Nov 2, 2026 |
FDIC / OCC (Federal Register) |
The European Banking Authority's June 2026 Risk Assessment Report specifically flags that frontier AI models, with enhanced ability to discover and exploit software vulnerabilities, are raising cyber-risk concerns among banks and supervisors, reinforcing existing DORA obligations around ICT risk management, third-party oversight, and resilience testing. In the US, the OCC and FDIC finalized a rule in September 2026 redirecting bank examiners toward material financial risk rather than procedural or documentation-only findings, a narrower supervisory lens that still requires banks to demonstrate their risk management is actually effective, not just documented.
The pattern across both is the same: a cyber incident, a vendor failure, or an AI misstep increasingly triggers obligations across several regulatory regimes at once. Platforms that keep risk, control, and evidence in one connected system, rather than siloed by department, are better positioned to answer what an event means across all of them simultaneously.
Industry Impact: Where GRC Demand Is Concentrated
GRC demand concentrates wherever regulatory exposure and operational complexity intersect. Financial services remains the deepest adopter: beyond the AI and cyber pressures above, banks operate under dense, overlapping regimes covering capital, anti-money-laundering obligations, and now AI-specific guidance, which rewards a platform able to connect a single risk event to every regime it touches rather than producing separate reports for each. Healthcare faces a similar bind from a different angle: privacy law, medical-device safety, data security, and heavy reliance on third-party vendors mean GRC has to span security, vendor oversight, and audit evidence at once. Technology companies have the opposite problem, which is speed new AI features can reach production faster than policy and risk review can keep pace, and that is exactly the gap that inventories of AI assets and automated control mapping are built to close.
Section summary: Demand is concentrated in sectors where regulatory density and operational complexity overlap most.
-
Financial services rewards platforms that connect one risk event to multiple regulatory regimes at once
-
Healthcare's GRC needs span vendor oversight, privacy, and security simultaneously
-
Technology companies need governance that can keep pace with AI features shipping faster than policy review
Vendors Are Shifting from Record-Keeping to Action
Competition in the GRC platform market spans diversified technology giants and dedicated specialists. NMSC's own competitive landscape names ServiceNow, Diligent, Wolters Kluwer, IBM, SAP, and Oracle building GRC into broader enterprise ecosystems, alongside specialists such as MetricStream, NAVEX, OneTrust, Workiva, Riskonnect, Vanta, and Drata competing on depth in audit, ESG, and continuous monitoring.
The more interesting shift is what these platforms now do. LogicGate's June 2026 release introduced Workflow Agents that handle repetitive compliance tasks, including evidence collection, control testing, and record linking, while keeping human sign-off on higher-impact judgments. That is a meaningful change from record-keeping software: the platform participates in the work rather than just storing proof it happened.
Section summary: The competitive edge in GRC software is moving from feature breadth to execution.
-
Enterprise suites are folding GRC into existing ERP ecosystems; specialists differentiate on ESG, audit, and third-party risk depth
-
AI agents are increasingly handling evidence collection and control testing, not just reporting
-
Human accountability remains the design constraint automation targets repetitive work, not high-impact decisions
Future Outlook for the GRC Platform Market
Looking ahead, three shifts stand out. First, continuous compliance is replacing point-in-time audit preparation, with automated evidence collection and control testing running year-round rather than intensifying each audit season. Second, AI is becoming both the subject of governance and a tool for doing it: platforms increasingly use AI to summarize risk and flag anomalies even as they govern other AI systems, a dual role that voluntary frameworks such as NIST's AI Risk Management Framework and ISO/IEC 42001 are starting to formalize. Third, GRC platforms are shifting from proving past compliance to informing forward decisions, helping leadership see which risks threaten specific business objectives before they materialize rather than which policies were followed after the fact. For a market already forecast to nearly double by 2030, that shift toward continuous, decision-oriented risk management is likely to matter more than any single feature addition.
Section summary: The next phase of growth favors platforms built for continuous, forward-looking risk management over periodic compliance checklists.
-
Continuous, automated evidence collection is replacing seasonal audit preparation
-
AI is both a governance target and a governance tool within the same platforms
-
The most valuable platforms will help leadership anticipate risk to specific objectives, not just document past compliance
Conclusion
The governance, risk, and compliance platform market is no longer a back-office compliance category. It is becoming the infrastructure that lets companies prove, continuously, that they are managing risk rather than just claiming to. With AI regulation, cyber risk, and financial-risk supervision all moving toward continuous, evidence-based standards at once, the businesses gaining ground are the ones treating GRC platforms as strategic infrastructure rather than an audit-season scramble.
About the Author
 Sanyukta Deb
— Sanyukta Deb is Digital Marketing Team Lead at Next Move Strategy Consulting, where she has led content strategy and technical SEO for the firm's B2B market research publications for over 2 years. Her editorial process translates NextMSC's primary and secondary research — spanning technology, industrial, and consumer sectors — into commercial narratives, backed by search-intent, keyword, and competitive analysis. She brings 5 years of overall experience in digital marketing and content strategy.
About the Reviewer
 Debashree Dey
— Debashree Dey is Assistant Manager at Next Move Strategy Consulting, where she supports cross-vertical market content and communications across diverse industries for 6 years. Her professional background includes senior content writing, communications, and published manuscript authorship, with experience developing audience-focused business narratives and maintaining clear, consistent messaging. Her role supports research-led content development and editorial quality across NextMSC publications.














Add Comment