Major GRC Challenges in Healthcare and How to Overcome Them
A single unpatched vendor connection, one lapsed Business Associate Agreement, or one over-privileged login can undo years of careful governance work at a hospital or health system. That is precisely why governance, risk, and compliance (GRC) teams in healthcare spend so much of their time on cybersecurity specifically and why the market built to serve that need is growing so fast. According to Next Move Strategy Consulting's Healthcare Cyber Security Market analysis, the global healthcare cybersecurity market was valued at USD 18.2 billion in 2023 and is projected to reach USD 62.1 billion by 2030, growing at a CAGR of 15.3% from 2024 to 2030.
Most of the practical GRC discipline behind that spending has not changed: organizations still need a clear regulatory inventory, a defined breach-response protocol, and consistent vendor risk assessments. Centralizing that work is exactly the gap that dedicated Healthcare GRC Software is built to close, automating regulatory tracking, policy review workflows, and Business Associate Agreement management rather than leaving them scattered across spreadsheets. What has changed over the past year is the market supplying the cybersecurity layer underneath that governance work, which is consolidating around identity security faster than almost any other category.
Why Healthcare Cybersecurity Spending Keeps Rising
Two forces are driving growth. The first is exposure: healthcare organizations run an expanding surface of electronic health records, connected medical devices, telehealth platforms, and third-party vendor portals, and each one is a potential entry point. According to NMSC's report, nearly 75% of ransomware attacks on the sector succeeded in encrypting data the highest rate in three years, up from 61% in 2022 which is precisely the failure mode a layered cybersecurity framework and a rehearsed breach-response plan are meant to prevent.
The second is a structural shift inside the cybersecurity industry itself: platform vendors are consolidating around identity security as the primary attack path, since AI adoption has multiplied the number of humans, machine, and now autonomous-agent identities that need governing. For a GRC team, that shift matters directly identity and access management sits at the center of HIPAA's minimum-necessary-access requirement, vendor Business Associate Agreements, and most breach post-mortems, so the platforms consolidating fastest are consolidating around exactly the control that healthcare compliance programs already treat as foundational.
Content key takeaways
In short: rising ransomware effectiveness and an industry-wide pivot to identity security are both pushing healthcare cybersecurity spending higher, and both map directly onto core GRC obligations rather than sitting apart from them.
-
The market is projected to more than triple from USD 18.2 billion (2023) to USD 62.1 billion by 2030
-
Ransomware encryption success rates reached a three-year high, reinforcing the need for rehearsed breach-response protocols
-
Cybersecurity vendors are consolidating around identity security, which overlaps directly with HIPAA access-control and vendor-risk requirements
-
Centralized GRC software addresses the process side of this problem; platform consolidation is addressing the technical side
Industry Leader Moves: The Identity Security Consolidation Wave
Next Move Strategy Consulting's Healthcare Cyber Security Market report tracks a set of key players, and the most consequential event of the past year involves two of them at once.
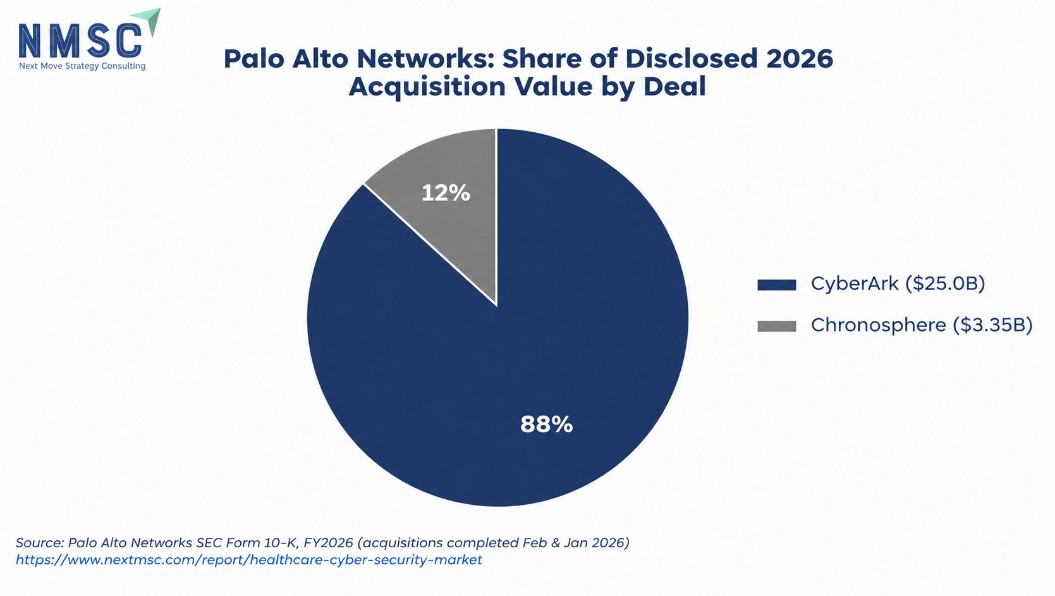
Palo Alto Networks Inc. completed its $25 billion acquisition of CyberArk on February 11, 2026, according to its own SEC filings, folding CyberArk's Identity Security Platform into a new identity-security pillar built to protect “every identity across the enterprise human, machine, and agentic,” in the companies' words. Palo Alto followed that deal with three more in quick succession: Chronosphere ($3.35 billion, January 2026, observability), Koi (April 2026, agentic endpoint security), and Portkey (May 2026, AI gateway security) a run of acquisitions that makes identity, not network perimeter, the center of its platform strategy.
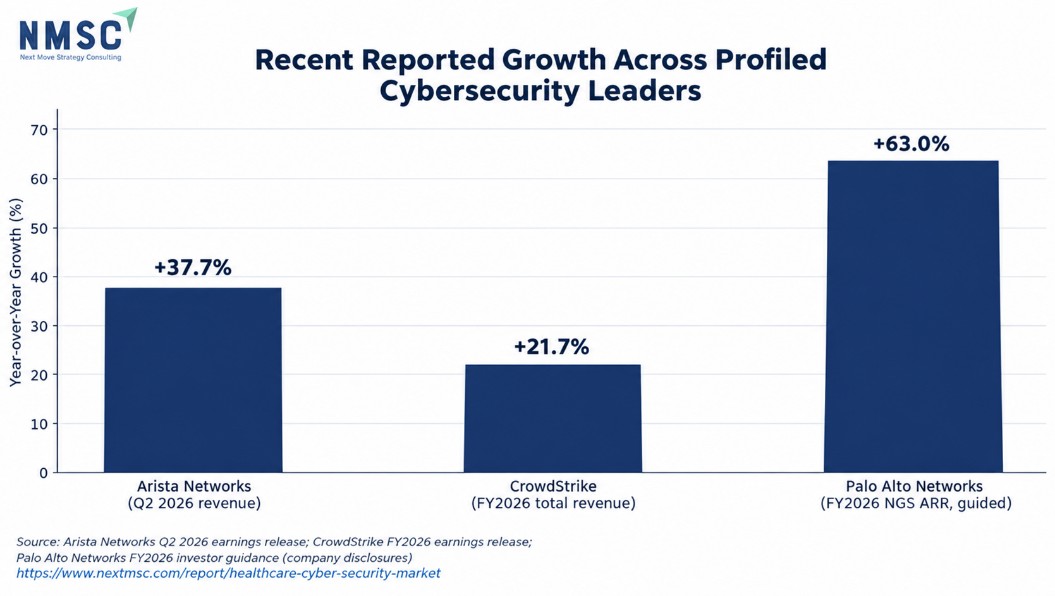
CrowdStrike Holdings answered with its own identity-security move, acquiring SGNL for $740 million in January 2026 an identity management startup specializing in real-time access revocation based on risk signals while reporting FY2026 revenue of $4.812 billion, up 21.7% year-on-year, and a record $330.7 million in net-new annual recurring revenue in its fourth quarter.
Check Point Software Technologies and Zscaler, Inc. both moved to secure the AI layer specifically: Check Point acquired LLM-security startup Lakera for $300 million, while Zscaler acquired managed-detection firm Red Canary for $675 million to add agentic security-operations capability to its zero-trust platform.
Fortinet, Inc. has continued building out Operational Technology (OT) security protecting the connected medical devices, infusion pumps, and building-management systems that sit alongside traditional IT in a hospital network through its Security Fabric architecture, which unifies firewalls, network access control, endpoint protection, and SIEM under one platform rather than requiring healthcare buyers to integrate point products themselves.
Arista Networks, Inc. posted a first-ever $3-billion revenue quarter in Q2 2026, up 37.7% year-on-year, and raised its full-year guidance to approximately $12.6 billion; alongside that growth, the company launched an AI-driven Edge Threat Management solution that unifies zero-trust security with SD-WAN for branch and satellite locations a relevant capability for multi-site health systems managing clinics and remote facilities.
Trend Micro Incorporated rebranded its enterprise security business as TrendAI in March 2026 and launched an Agentic Governance Gateway to give security teams visibility and control over autonomous AI agents operating across enterprise systems; in August 2026, the unit reported surpassing $1 billion in cumulative Amazon Web Services Marketplace sales, pointing to a deepening AI-security co-selling relationship between the two companies.
Cisco Systems and Microsoft Corporation both extended security into their broader AI-agent platforms rather than treating it as a separate product: Cisco unveiled Cloud Control at Cisco Live US in June 2026, a unified platform for managing networking, security, and observability across both human administrators and AI agents, while Microsoft's Agent 365, made generally available in May 2026, gives IT teams a governance layer for discovering and securing AI agents operating with their own credentials the same access-governance problem GRC teams already manage for human users. IBM Corporation's watsonx Orchestrate followed the same logic in May 2026, evolving into what IBM calls an “agentic control plane” that can govern agents built on any vendor's framework.
Gen Digital Inc. the company most people still know by its earlier name, NortonLifeLock, before its 2022 rebrand continues to operate its Norton, Avast, and LifeLock portfolio at a $5.0 billion revenue scale, though no material, publicly disclosed healthcare-specific development was identified for the company in the past six months.
Industry Impact key takeaways
In short: the defining move of the past year is Palo Alto Networks' $25 billion acquisition of CyberArk, and nearly every other profiled leader is chasing the same identity- and agent-governance opportunity from a different angle.
-
Palo Alto Networks and CyberArk's combination is the single largest, most consequential move among the profiled companies
-
CrowdStrike, Check Point, and Zscaler have each made a dedicated identity- or AI-security acquisition within the same window
-
Cisco, Microsoft, and IBM are all building agent-governance capability directly into their broader platforms rather than selling it separately
-
Fortinet and Arista are extending security into OT and multi-site network contexts especially relevant to distributed health systems
Healthcare Cyber Security Market: Report Scope and Segmentation
|
Parameter |
Detail |
|
Market Size in 2023 |
USD 18.2 Billion |
|
Revenue Forecast in 2030 |
USD 62.1 Billion |
|
Growth Rate |
CAGR of 15.3% from 2024 to 2030 |
|
Analysis Period |
2023–2030 |
|
Base Year Considered |
2023 |
|
Countries Covered |
28 |
|
Companies Profiled |
10 |
|
Growth Factors |
Rising incidents of cyber-attacks; increasing government investment in healthcare cybersecurity |
Industry Leader Moves at a Glance
|
Company |
Recent Move |
When |
Source |
|
Palo Alto Networks / CyberArk |
$25B acquisition completed, forming next-gen identity security platform |
Feb 2026 |
Palo Alto Networks SEC Form 8-K |
|
CrowdStrike Holdings |
$740M acquisition of identity-security startup SGNL; record net-new ARR |
Jan 2026 |
CrowdStrike earnings release |
|
Check Point Software |
$300M acquisition of LLM-security startup Lakera |
2025–2026 |
Company disclosures |
|
Zscaler, Inc. |
$675M acquisition of Red Canary for agentic SOC capability |
August 2025 |
Company disclosures |
|
Fortinet, Inc. |
Continued OT/medical-device security build-out via Security Fabric |
Ongoing |
Fortinet product documentation |
|
Arista Networks, Inc. |
First $3B+ revenue quarter (+37.7% YoY); AI-driven Edge Threat Management launch |
Q2 2026 |
Arista Networks earnings release |
|
Trend Micro Incorporated |
Rebranded enterprise unit as TrendAI; surpassed $1B in AWS Marketplace sales |
Mar & Aug 2026 |
Trend Micro Newsroom |
|
Cisco Systems |
Launched Cisco Cloud Control, unified agentic security/networking platform |
Jun 2026 |
Cisco Newsroom |
|
Microsoft Corporation |
Agent 365 general availability for AI-agent identity governance |
May 2026 |
Microsoft Newsroom |
|
IBM Corporation |
watsonx Orchestrate evolved into a cross-vendor agentic control plane |
May 2026 |
IBM Newsroom |
Future Outlook
Identity is likely to remain the center of gravity. That is also the clearest link to Next Move Strategy Consulting's Healthcare Identity and Access Management Market research, which tracks the access-governance tools many now being absorbed into the platforms discussed above that map directly onto the identity and access controls healthcare compliance programs are already required to maintain.
Three other trends look set to continue. First, expect further consolidation: once one platform vendor completes a landmark identity-security acquisition, competitors tend to respond within months rather than years, as CrowdStrike's, Check Point's, and Zscaler's own deals already show. Second, agent governance securing and auditing AI agents that act with their own credentials is quickly becoming a distinct healthcare compliance requirement, not just a cybersecurity feature, since an ungoverned agent with access to patient data raises the same HIPAA questions as an ungoverned employee account. Third, OT and medical-device security will keep gaining priority as more clinical equipment connects to hospital networks, an area where Fortinet and similar vendors are investing specifically.
Future Outlook key takeaways
In short: identity and agent governance are converging with core GRC obligations, and further platform consolidation should be expected rather than treated as a one-off.
-
Expect continued M&A activity centered on identity and AI-agent security among the profiled leaders
-
Expect AI agent governance to become a distinct healthcare compliance requirement, not just a security feature
-
Expect OT and connected medical-device security to keep gaining investment priority
-
Expect identity and access management tooling to keep converging with core GRC and vendor-risk processes
Conclusion
The healthcare cybersecurity market's path to a projected USD 62.1 billion by 2030 is, at its core, a story about identity: who or what has access to patient data, and who is watching that access closely enough to catch a problem before it becomes a breach. Palo Alto Networks' acquisition of CyberArk is the clearest signal of where the platform vendors are placing their bets, but the underlying discipline it points back to is one every healthcare GRC team already recognizes: map your risk, centralize your governance, and treat access control as the foundation everything else is built on.
Curious how these figures break down by solution, security type, and end user? Download Free Sample of NMSC's full Healthcare Cyber Security Market report.
About the Author
 Sanyukta Deb
— Sanyukta Deb is Digital Marketing Team Lead at Next Move Strategy Consulting, where she has led content strategy and technical SEO for the firm's B2B market research publications for over 2 years. Her editorial process translates NextMSC's primary and secondary research — spanning technology, industrial, and consumer sectors — into commercial narratives, backed by search-intent, keyword, and competitive analysis. She brings 5 years of overall experience in digital marketing and content strategy.
About the Reviewer
 Debashree Dey
— Debashree Dey is Assistant Manager at Next Move Strategy Consulting, where she supports cross-vertical market content and communications across diverse industries for 6 years. Her professional background includes senior content writing, communications, and published manuscript authorship, with experience developing audience-focused business narratives and maintaining clear, consistent messaging. Her role supports research-led content development and editorial quality across NextMSC publications.










Add Comment