Japan Healthcare Cybersecurity Market By Component (Software, Hardware, and Services), By Deployment Model (Cloud, On-Premises, and Hybrid), By Organization Size (Small, Medium, and Large), By Commercial Model (Subscription, Perpetual License, Consumption Based, Appliance Sale, Project-Based, Managed Service Contract, and Support Contract), By Customer Type, By Buyer Type, and By Sales Channel – Opportunity Analysis & Forecast, 2025-2035
Industry: Healthcare | Latest Edition: August 13, 2026 | No of Pages: 311 | No. of Tables: 164 | No. of Figures: 52 | Format: PDF | Report Code : HC4082
What Is the Japan Healthcare Cybersecurity Market Size?
The Japan Healthcare Cybersecurity Market was valued at USD 1.38 billion in 2025, is estimated at USD 1.80 billion in 2026, and is projected to reach USD 5.93 billion by 2035 at a 14.15% CAGR from 2026 to 2035. Software is the dominant segment, driven by identity and endpoint controls.
|
Key Takeaways |
|
By Component: Software is the dominant segment, while Services is the fastest-growing segment. |
|
By Deployment Model: On-Premises is the dominant segment, while Cloud is the fastest-growing segment. |
|
By Organization Size: Large is the dominant segment, while Small is the fastest-growing segment. |
|
By Commercial Model: Subscription is the dominant segment, while Managed Service Contract is the fastest-growing segment. |
|
By Customer Type: Healthcare Providers is the dominant segment, while Medical Technology is the fastest-growing segment. |
|
By Buyer Type: Chief Information Security Officer is the dominant segment, while Biomedical Engineering is the fastest-growing segment. |
|
By Sales Channel: Direct Sales is the dominant segment, while Managed Security Service Providers is the fastest-growing segment. |
Market Opportunity: The Japan Healthcare Cybersecurity Market is expected to create an absolute dollar opportunity of USD 4.13 billion between 2026 and 2035, which underscores the upside in identity-first, managed, and medical-device security programs.
According to NMSC’s analysis, buyers are increasingly consolidating tools into fewer security platforms so they can improve visibility across clinical networks, cloud workloads, and connected medical devices without expanding operational complexity.
What does the Japan Healthcare Cybersecurity Market Encompass?
The Japan Healthcare Cybersecurity Market encompasses software, hardware, and services used to protect healthcare providers, payers, life sciences firms, medical technology companies, and public institutions from unauthorized access, ransomware, data leakage, and operational disruption. It spans identity security, endpoint protection, network security, cloud security, application security, data security, email security, security operations, exposure management, and operational technology security, along with appliances and managed services that support those controls. The market now centers on continuous defense rather than one-time product installation.
Our assessment indicates that the market has evolved from compliance-led procurement into a resilience-led architecture model shaped by healthcare continuity risk, hybrid IT, and connected clinical workflows. Japan’s Ministry of Health, Labour and Welfare and the Ministry of Economy, Trade and Industry have both reinforced security guidance for medical information systems and service providers, which has raised the importance of authentication, logging, incident response, and business continuity planning. Technology adoption is accelerating around zero trust, cloud visibility, and monitoring for medical devices and other operational technology.
|
Parameter |
Details |
|
Market Size in 2025 |
USD 1.38 Billion |
|
Market Size in 2026 |
USD 1.80 Billion |
|
Revenue Forecast in 2035 |
USD 5.93 Billion |
|
Growth Rate |
CAGR of 14.15% from 2026 to 2035 |
|
Analysis Period |
2025–2035 |
|
Base Year Considered |
2025 |
|
Forecast Period |
2026–2035 |
|
Market Size Estimation |
USD Billion |
|
Companies Profiled |
15 |
|
Market Share |
Available for Top 10 Companies |
Key Emerging Trends
Based on research conducted by NMSC, we found that four structural trends are reshaping buying patterns, product design, and channel strategy across the Japan Healthcare Cybersecurity Market.
How Are Zero Trust Identity Controls Reshaping Hospital Access?
We observed that hospitals are tightening access control around electronic medical records, remote clinical workflows, and administrator privileges by prioritizing multi-factor authentication, single sign-on, and privileged access management. This shift reduces credential abuse and supports auditability across multi-site care networks. For example, the Ministry of Health, Labour and Welfare’s updated medical information security guidance has made stronger authentication and operational controls a practical baseline for providers modernizing security stacks.
Why Are Managed Detection and Response Models Gaining Share?
During our Japan Healthcare Cybersecurity market evaluation, we noticed that healthcare operators increasingly favor managed security services because 24-hour monitoring and incident response are difficult to build in-house. This is especially relevant for regional hospitals and mid-sized clinics that need SOC coverage, threat hunting, and firewall administration without adding full internal teams. For example, Cisco’s hospital collaboration in Japan around XDR and SOC design shows how outsourced security operations are moving into clinical environments.
How Is Cloud Modernization Changing Security Architecture?
We found that cloud migration is expanding the need for cloud security posture management, workload protection, and secure remote access across healthcare IT estates. Hybrid operating models are now common because hospitals must connect legacy systems, SaaS platforms, and remote care services while preserving data control. For example, cloud marketplaces and subscription-delivered controls are making it easier for providers to adopt new protections without large appliance refresh cycles.
What Is Driving OT And Medical Device Security Adoption?
NMSC’s analysis indicates that connected diagnostics, imaging systems, and biomedical equipment are expanding the attack surface beyond traditional IT. Healthcare organizations are responding with passive sensors, segmentation, and medical device security tools that can monitor traffic without disrupting clinical workflows. For example, vendor medical IoT security offerings illustrate how the Japan Healthcare Cybersecurity market is moving toward device-aware controls that protect patient care continuity as well as data integrity.
Strategic Framework of the Japan Healthcare Cybersecurity Market
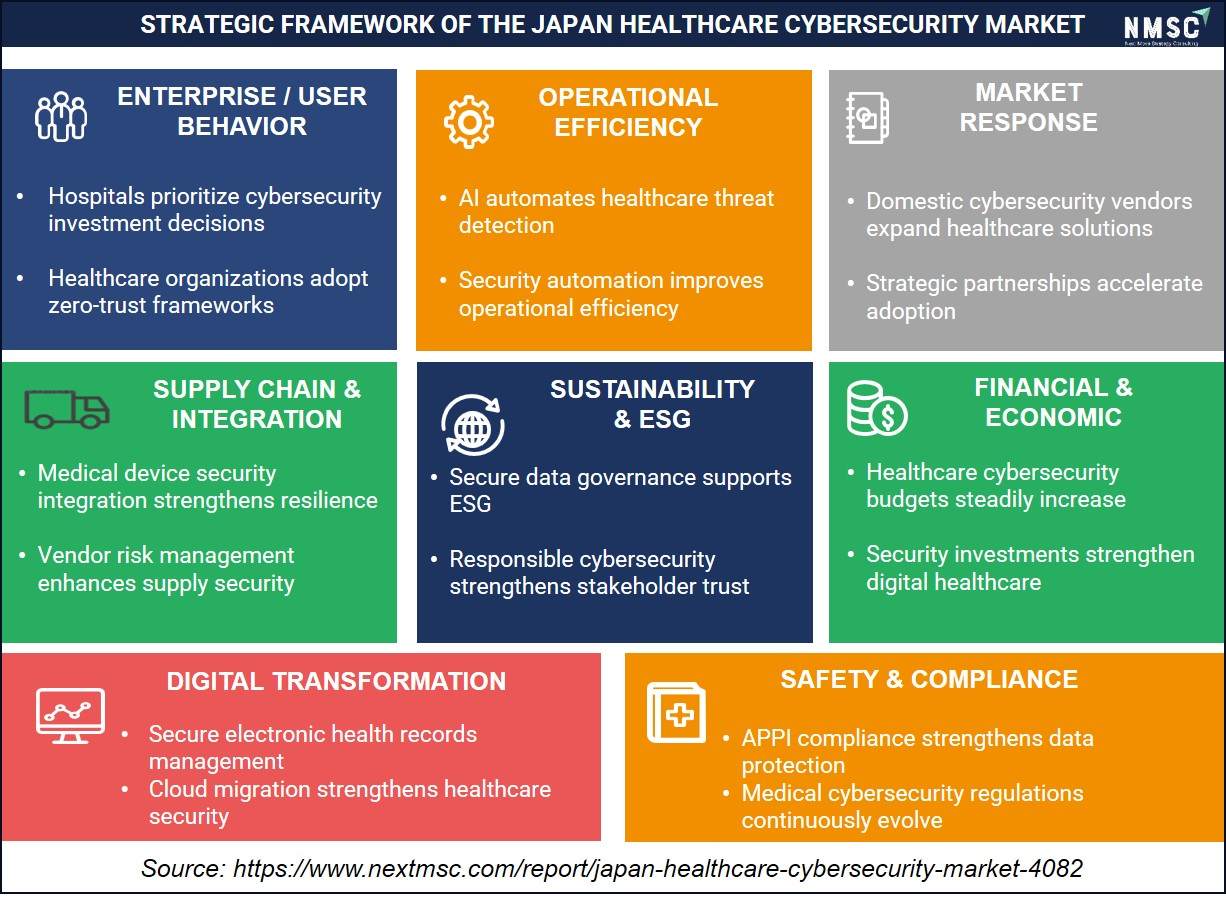
This infographic presents the strategic framework of the Japan healthcare cybersecurity market, highlighting the key factors driving market growth and resilience. It illustrates how enterprise cybersecurity adoption, AI-enabled operational efficiency, strategic vendor partnerships, secure supply chain integration, ESG-focused data governance, increasing cybersecurity investments, digital transformation, and evolving regulatory compliance collectively strengthen healthcare security, improve operational performance, enhance patient data protection, and support the continued modernization of Japan’s digital healthcare ecosystem.
Growth Drivers & Restraints
|
Factors |
Type |
(+/-) % Impact on CAGR |
Geographic Relevance |
Impact Timeline |
|
Zero trust identity modernization |
Driver |
+2.3% |
Nationwide; strongest in large hospitals |
2026–2030 |
|
Managed detection and response outsourcing |
Driver |
+2.1% |
Nationwide; strongest in regional providers |
2026–2035 |
|
Medical device and OT segmentation |
Driver |
+1.9% |
Large hospitals and medtech sites |
2026–2031 |
|
Legacy system integration complexity |
Restraint |
−1.6% |
Small and medium providers |
2026–2030 |
|
Budget fragmentation and slow procurement |
Restraint |
−1.3% |
Public and regional hospitals |
2026–2032 |
|
Security skills shortage |
Restraint |
−1.4% |
Nationwide |
2026–2030 |
|
Cloud and hybrid modernization |
Driver |
+1.5% |
Nationwide |
2026–2035 |
What Is the Primary Growth Driver of Japan Healthcare Cybersecurity Market?
The strongest driver is the rising need to protect patient data and maintain clinical continuity as ransomware, credential theft, and service disruption threats intensify. Japan’s Ministry of Health, Labour and Welfare updated its medical information security guidance to version 7.0 in June 2026, which reinforces the importance of authentication, logging, incident response, and backup recovery. IPA’s 2025 security white paper also highlights continued ransomware, supply chain, and GenAI-enabled threats in 2024, supporting sustained demand for stronger controls.
How Is Threat Complexity Driving The Market Growth of Japan Healthcare Cybersecurity Market?
Attackers are targeting healthcare through identity abuse, email phishing, remote access weaknesses, and exploitation of connected devices, which forces organizations to broaden coverage across endpoint, network, cloud, and data layers. We observed that this complexity is pushing buyers toward integrated suites and managed services rather than standalone tools. Industry-derived estimate: the shift to broader platform adoption is likely to lift multi-year contract values as hospitals seek fewer vendors and faster incident response.
What Is Restraining The Japan Healthcare Cybersecurity Market?
Legacy infrastructure, fragmented procurement, and the operational burden of integrating security across mixed vendor environments continue to slow adoption, particularly in smaller institutions. Industry-derived estimate: a meaningful share of regional hospitals still manages aging systems, specialized medical devices, and third-party service layers that do not refresh on the same cycle, which raises implementation time and increases the cost of uniform zero trust rollouts.
Segmentation Analysis
By Component Insights
How Is the Component Mix Structured?
Based on Component, the Japan Healthcare Cybersecurity Market is divided into Software, Hardware, and Services. Software leads because healthcare buyers need immediate control over identities, endpoints, networks, data, and cloud access across hospital and provider environments. Hardware remains important where appliances and passive sensors are required, but it is usually purchased as part of a broader stack. Services are increasingly bundled with software because healthcare operators want managed monitoring, consulting, and maintenance that fit lean internal security teams.
The dominant sub-segment is Software, while Services is the fastest-growing sub-segment because healthcare organizations want ongoing detection, response, and support rather than one-time deployment. Identity security and endpoint security are especially influential within software spending because they address the most common access and malware risks. On the services side, managed security and support contracts are expanding as hospitals and life sciences firms seek predictable operating costs and faster incident handling.
By Deployment Model Insights
How Are Deployment Preferences Changing?
Based on Deployment Model, the market is organized across Cloud, On-Premises, and Hybrid environments. On-premises security remains deeply embedded in Japan’s healthcare sector because hospitals often retain legacy clinical systems and prefer direct control over sensitive patient data. Hybrid deployments are now common where organizations must connect older environments to newer cloud services without disrupting patient workflows. Cloud adoption is still accelerating as providers look for faster deployment and lower capital intensity.
The dominant deployment model is On-Premises, while Cloud is the fastest-growing model as healthcare organizations modernize their IT estates and shift selected workloads to subscription-based platforms. Hybrid architectures are the bridge between these two realities, especially for large hospitals that need data locality, resilience, and access to new analytics tools. The fastest gains are coming from cloud-first security controls that can support remote access, SaaS adoption, and centralized monitoring.
Growth Opportunities
Based on research conducted by NMSC, we found that three forward-looking opportunities are reshaping buying patterns, product design, and channel strategy across the Japan Healthcare Cybersecurity Market.
Where Can Identity Governance Expand New Security Budgets?
Identity governance and privileged access programs present a clear whitespace opportunity because they reduce the risk created by shared accounts, remote logins, and over-privileged administrator access. The beneficiary segment is healthcare providers, especially large hospitals and multi-facility groups that must prove who accessed patient data, when, and from where. Vendors that package IGA, PAM, MFA, and SSO into one operational workflow can win upgrade cycles.
How Can Managed Security Services Penetrate Mid-Market Care Networks?
Managed security service contracts are a strong opportunity because many regional hospitals and clinics need continuous monitoring but cannot staff a full internal security operations team. The beneficiary segment is small and medium healthcare providers, along with systems integrators and MSSPs that can deliver detection, response, firewall operations, and endpoint oversight. Bundled services reduce procurement friction and make recurring revenue more durable.
Why Does Medical Device Security Create A Distinct Whitespace?
Medical device security and clinical IoT monitoring create a specialized opportunity because connected equipment expands the attack surface inside hospitals and diagnostic centers. The beneficiary segment is medical technology, along with healthcare providers that run large device fleets. Passive network sensors, segmentation, and device-aware monitoring can protect clinical uptime without disrupting care delivery, which makes the offer easier to justify to engineering and biomedical teams.
Ecosystem Analysis of the Japan Healthcare Cybersecurity Market
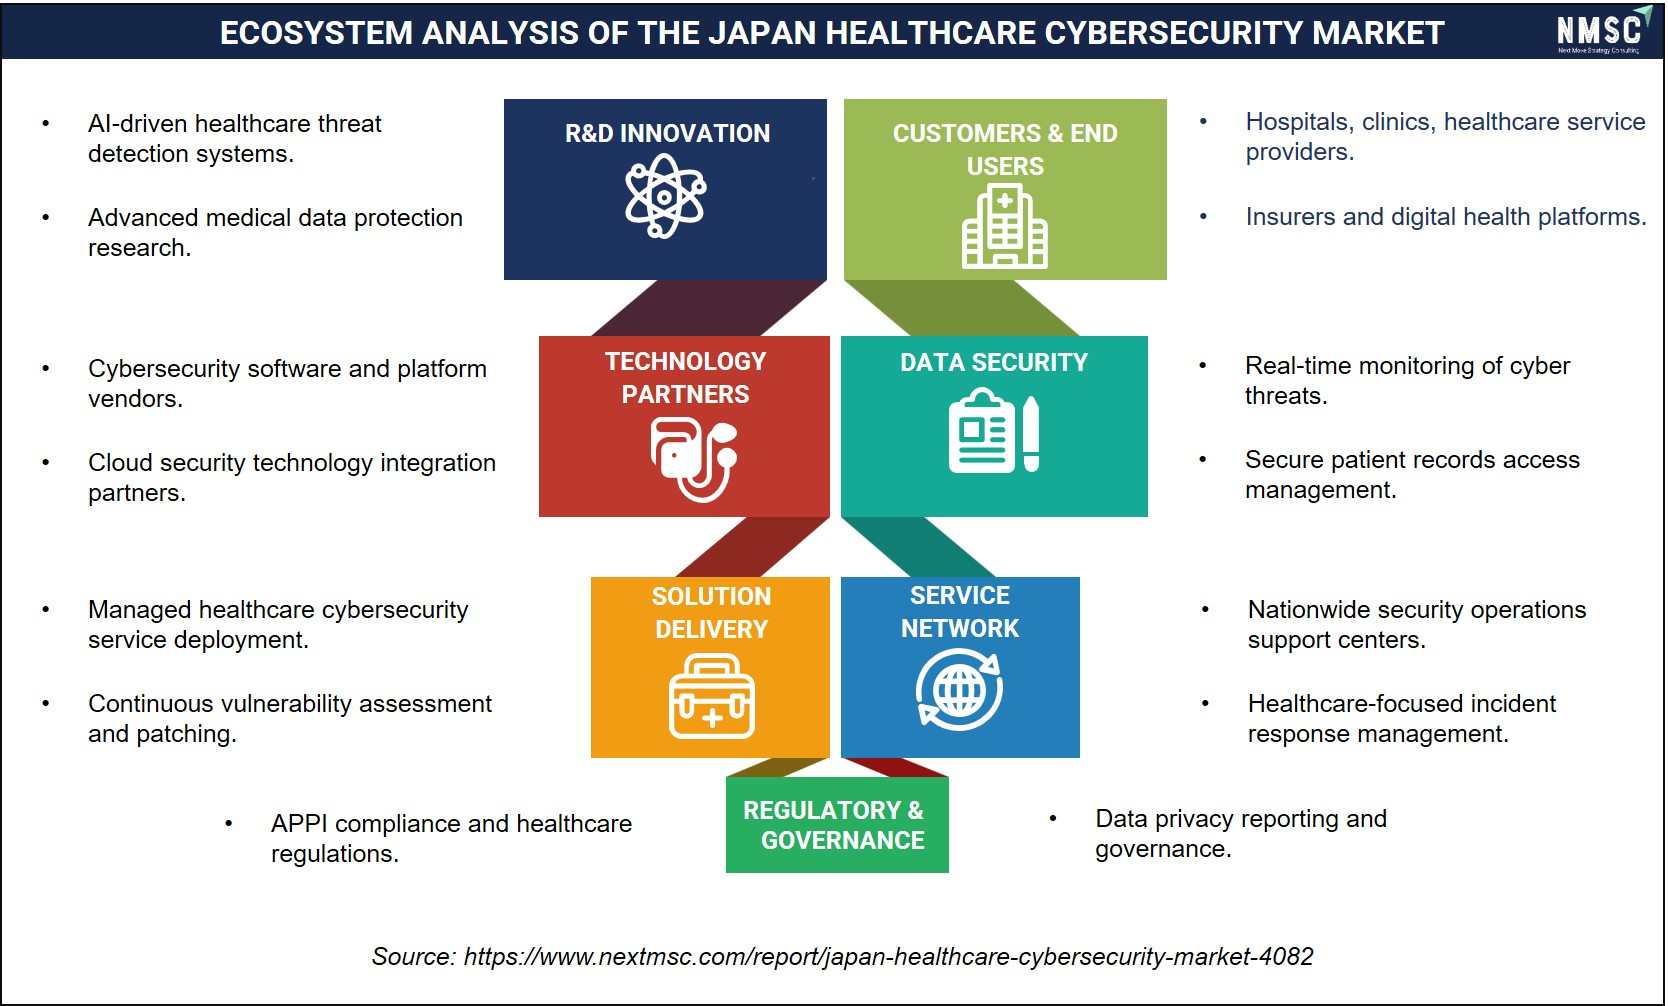
This infographic illustrates the ecosystem analysis of the Japan healthcare cybersecurity market, highlighting the interconnected stakeholders that drive market development. It showcases the roles of R&D and innovation, technology partners, data security providers, solution delivery firms, service networks, regulatory and governance bodies, and healthcare end users. The ecosystem demonstrates how collaboration among technology developers, healthcare providers, insurers, and regulatory authorities strengthens cybersecurity capabilities, safeguards sensitive health data, and supports the secure digital transformation of Japan’s healthcare sector.
Competitive Landscape
We observed that the Japan Healthcare Cybersecurity Market is highly competitive, but competition is not evenly distributed because platform vendors, identity specialists, network security providers, and service integrators each solve a different part of the clinical risk stack.
|
Dimension |
Description |
|
Market Structure |
Highly competitive, with global platform vendors, specialist cybersecurity providers, and local channel partners competing on coverage, compliance support, and operational simplicity. |
|
Innovation Focus |
Identity security, XDR, cloud protection, exposure management, and OT-aware monitoring dominate product roadmaps because healthcare buyers want fewer blind spots and faster response. |
|
M&A Activity |
Acquisitions are consolidating identity, endpoint, and exposure management capabilities, which encourages platform bundling and more aggressive cross-sell motion across enterprise accounts. |
How Do Companies Compete in the Japan Healthcare Cybersecurity Market?
Companies compete by combining technical breadth with healthcare-specific execution. Global vendors such as Palo Alto Networks, Cisco, Fortinet, CrowdStrike, Microsoft, Trend Micro, and Check Point emphasize integrated security platforms, while IBM, Zscaler, Arista, Splunk, Trellix, Sophos, CyberArk, and Okta compete on specialist depth. Pricing is increasingly subscription-led, but vendors still use appliance bundles and professional services to match hospital procurement patterns.
Which Competitive Archetypes Dominate the Industry?
Two archetypes dominate the industry. The first is the platform-led vendor that sells network, endpoint, identity, cloud, and operations controls as one stack, which helps healthcare buyers reduce integration overhead. The second is the specialist vendor or integrator that wins on niche depth, such as identity governance, secure remote access, or managed detection. Geographic expansion is strongest in Tokyo, Osaka, and other dense care markets.
How Are Vendors Differentiating Through Innovation?
Vendors are differentiating through automation, device awareness, and security operations integration. We found that AI-assisted analytics, zero trust access, cloud posture management, and passive monitoring for medical devices are now central selling points. Companies that can link these features to measurable outcomes such as lower downtime, fewer privileged accounts, and faster containment are better positioned to protect pricing and defend share in renewal cycles.
What M&A Activity Is Shaping The Market?
M&A is reshaping the Japan Healthcare Cybersecurity market by collapsing functionality into broader security platforms and increasing pressure on point-solution vendors. Acquisitions in identity, exposure management, and SOC tooling help large suppliers offer more complete bundles to healthcare buyers. The result is a more concentrated competitive field where scale, channel reach, and healthcare reference wins matter as much as product features.
Key Market Players
We observed that the following companies are actively shaping security spending, platform adoption, and channel dynamics within the Japan Healthcare Cybersecurity Market.
-
Fortinet Japan G.K.
-
CrowdStrike Japan G.K.
-
Check Point Software Technologies K.K.
-
Microsoft Japan Co., Ltd.
-
Zscaler Japan K.K.
-
IBM Japan, Ltd.
-
Trend Micro Incorporated
-
Arista Networks Japan K.K.
-
Splunk Services Japan G.K.
-
Trellix Japan K.K.
-
Sophos K.K.
-
CyberArk Software K.K.
-
Okta Japan K.K.
Latest Developments
We found that recent developments in Japan are centered on stricter medical-information guidance, hospital security collaborations, and regional vendor expansion.
|
Date |
Event |
|
November 2024 |
Cisco, Maebashi Red Cross Hospital, and Uniadex announced a collaboration to enhance hospital network security and implement SOC capabilities. |
Investment Opportunities
Our findings suggest that three investment themes will attract the most attention over the forecast period.
Where Are Capital Inflows Concentrating?
Capital inflows are concentrating on identity security, managed detection and response, and cloud-native platforms because these categories map directly to healthcare continuity risk. We observed that investors favor vendors with recurring revenue, strong healthcare reference accounts, and clear compliance relevance. The market’s 2026 value of USD 1.80 billion and its projected 2035 value of USD 5.93 billion make long-duration platform investments especially attractive.
How Does Infrastructure Investment Support The Market?
Infrastructure investment is flowing into secure networks, centralized logging, cloud governance, backup resilience, and device-aware monitoring. Our findings suggest that hospitals and life sciences operators are prioritizing architecture that can support remote access, hybrid work, and connected care without compromising uptime. The most durable investments are those that reduce tool sprawl and improve incident response across clinical and administrative systems.
What ESG Considerations Influence Investment Decisions?
ESG considerations are increasingly tied to patient safety, data stewardship, and responsible procurement. We found that investors and boards view cybersecurity as a social and governance issue because service outages can disrupt treatment, while poor controls can damage trust. Vendors that improve resilience, reduce duplicated hardware, and support longer asset life through software-led consolidation can strengthen both operating efficiency and ESG narratives.
Key Benefits for Stakeholders
How Does This Report Benefit Enterprise And Industry Leaders?
Enterprise and industry leaders gain a structured view of where security spend is most likely to rise across software, hardware, services, deployment models, and customer groups. The report helps them benchmark current posture against market direction, prioritize continuity-critical investments, and align security architecture with clinical operations. That makes strategic planning, vendor selection, and budget allocation more defensible.
How Does This Report Benefit Investors And Financial Analysts?
Investors and financial analysts gain a consistent Japan Healthcare Cybersecurity market size framework, a 2025 to 2035 growth path, and a clear view of which commercial models and customer types are likely to compound value. We found that this combination is especially useful for assessing recurring revenue quality, channel leverage, and the durability of platform adoption in a regulated healthcare environment.
How Does This Report Benefit Technology Vendors And Product Teams?
Technology vendors and product teams gain practical direction on which capabilities matter most in Japan’s healthcare environment, including identity governance, endpoint defense, cloud visibility, exposure management, and OT monitoring. Our analysis shows that this helps teams shape roadmaps, build partner strategies, and target customer segments with the strongest need for resilient, clinically aligned cybersecurity.
Key Market Segments
By Component
-
Software
-
Identity Security
-
Identity Governance and Administration
-
Privileged Access Management
-
Multi-Factor Authentication
-
Single Sign-On
-
Identity Threat Detection and Response
-
-
Endpoint Security
-
Endpoint Protection
-
Endpoint Detection and Response
-
Extended Detection and Response
-
Mobile Threat Defense
-
-
Network Security
-
Network Firewall
-
Network Detection and Response
-
Network Access Control
-
Secure Remote Access
-
Network Segmentation
-
-
Cloud Security
-
Cloud Security Posture Management
-
Cloud Workload Protection
-
Cloud Access Security Broker
-
Container Security
-
Kubernetes Security
-
-
Application Security
-
Web Application Firewall
-
API Security
-
Runtime Application Protection
-
Application Security Testing
-
-
Data Security
-
Data Loss Prevention
-
Encryption
-
Database Security
-
File Security
-
Tokenization
-
-
Email Security
-
Secure Email Gateway
-
Anti-Phishing
-
Business Email Protection
-
Email Encryption
-
-
Security Operations
-
Security Information and Event Management
-
Automation and Response
-
Threat Intelligence
-
Log Management
-
Threat Hunting
-
-
Exposure Management
-
Vulnerability Management
-
Attack Surface Management
-
Configuration Compliance
-
Security Validation
-
-
Operational Technology Security
-
Medical Device Security
-
Clinical Internet of Things Security
-
Network Monitoring
-
Biomedical Asset Protection
-
-
Other Security Software
-
-
Hardware
-
Network Security Appliances
-
Firewall Appliances
-
Secure Web Gateways
-
Secure Remote Access Appliances
-
-
Identity Security Appliances
-
Hardware Security Modules
-
Authentication Appliances
-
-
OT Security Appliances
-
Passive Network Sensors
-
Dedicated Monitoring Appliances
-
-
Other Security Hardware
-
-
Services
-
Managed Security Services
-
Detection and Response
-
Security Operations Center
-
Firewall
-
Endpoint Security
-
Cloud Security
-
Exposure Management
-
Other Managed Security Services
-
-
Professional Services
-
Security Consulting
-
Risk Assessment
-
Compliance Advisory
-
Security Architecture
-
Deployment
-
System Integration
-
Incident Response
-
Digital Forensics
-
Security Awareness Training
-
Other Professional Services
-
-
Support and Maintenance
-
Technical Support
-
Software Maintenance
-
Hardware Maintenance
-
Premium Support
-
-
By Deployment Model
-
Cloud
-
On-Premises
-
Hybrid
By Organization Size
-
Small
-
Medium
-
Large
By Commercial Model
-
Subscription
-
Perpetual License
-
Consumption Based
-
Appliance Sale
-
Project-Based
-
Managed Service Contract
-
Support Contract
By Customer Type
-
Healthcare Providers
-
Integrated Delivery Networks
-
General Hospitals
-
Specialty Hospitals
-
Physician Practices
-
Ambulatory Surgery Centers
-
Diagnostic Imaging Centers
-
Long-Term Care Facilities
-
Home Healthcare Providers
-
-
Healthcare Payers
-
Commercial Health Insurers
-
Government Health Payers
-
-
Life Sciences
-
Pharmaceutical Companies
-
Biotechnology Companies
-
Contract Research Organizations
-
-
Medical Technology
-
Medical Device Manufacturers
-
Digital Health Companies
-
-
Healthcare Public Sector
-
Public Health Agencies
-
Academic Medical Centers
-
Research Institutes
-
By Buyer Type
-
Chief Information Officer
-
Chief Information Security Officer
-
Information Technology Infrastructure
-
Security Operations Center
-
Clinical Engineering
-
Biomedical Engineering
-
Risk and Compliance
-
Procurement
By Sales Channel
-
Direct Sales
-
Value-Added Resellers
-
Systems Integrators
-
Managed Security Service Providers
-
Cloud Marketplaces
-
Original Equipment Manufacturer Partners
Conclusion & Recommendations
Long-Term Outlook
The long-term outlook remains strong because healthcare organizations must defend patient data, preserve clinical uptime, and modernize fragmented infrastructure at the same time. We observed that the market’s move from isolated tools to integrated platforms will continue through 2035, especially as cloud usage, remote access, and connected devices expand the attack surface. The result is durable demand across software and managed services.
Strategic Positioning Recommendations
Vendors should position around identity-first control, endpoint visibility, and managed response rather than feature-by-feature competition. Our assessment indicates that healthcare buyers prefer fewer vendors, clearer accountability, and faster operational handoff. Companies that combine healthcare references, Japanese-language support, and strong partner ecosystems will be better placed to win large hospital accounts and regional rollouts.
Investment Attractiveness
The market is attractive for investors because it combines regulation-led demand with recurring subscription and service revenue. We found that demand is likely to remain resilient even when hospital budgets tighten, since downtime and data exposure create direct clinical and financial consequences. The 2026 market size of USD 1.80 billion and the 2035 forecast of USD 5.93 billion support a long runway for capital deployment.
Market Shifts and Key Risks
The biggest shifts are consolidation, hybridization, and the rise of medical-device security. Key risks include procurement delays, legacy integration costs, and the possibility that buyers defer upgrades when staffing is thin. We observed that the vendors most exposed to these risks are those that rely on narrow point solutions without operational support or clear healthcare use cases.
Growth Pathways
Growth pathways center on platform bundles, managed services, device-aware monitoring, and cloud-ready security controls. NMSC’s analysis indicates that the fastest value creation will come from vendors that connect technical functionality to measurable outcomes such as lower downtime, stronger audit trails, and faster containment. Those capabilities align closely with how Japanese healthcare buyers evaluate risk and resilience.


About the Author
 Liza Phukan is Research Associate at Next Move Strategy Consulting, where she has covered emerging industries and market research across sectors for 3.5 years. Her work includes analyzing industry developments, validating market data, and developing structured business content from research findings. She uses secondary research and data-validation practices to turn complex market information into clear decision-useful market analysis for business audiences and support report development and B2B.
About the Reviewer
 Supradip Baul is an accomplished business consultant and strategist with over a decade of rich experience in market intelligence, strategy, technology, and business transformation. His work has included rigorous qualitative and quantitative analysis across multiple industries, helping clients shape investment decisions and long-term roadmaps. Earlier in his career, he was associated with Gartner, where he contributed to industry-leading reports and market share analyses. He has worked with leading global companies and holds an MBA with a dual specialization in Marketing and Finance.
At Next Move Strategy Consulting, we understand that insightful market research is the cornerstone of successful business decisions. That's why we employ a robust and multifaceted approach, combining various methodologies to deliver the most accurate and actionable data for our clients.

Research Landscape
We navigate the world of research with two primary approaches:
Qualitative Approach
Our qualitative research methodologies involve immersive techniques such as in-depth interviews, focus groups, and observational studies. By engaging directly with individuals and stakeholders, we uncover valuable insights that quantitative data alone may overlook.

Quantitative Research
In tandem with qualitative methodologies, NMSC leverages the power of Quantitative Research to provide a robust foundation of numerical insights. Through systematic data collection and analysis, we quantify patterns, preferences, and market trends, offering a comprehensive view of the business landscape.
Our quantitative research approach employs diverse tools, including surveys, experiments, and statistical modelling. These methodologies enable us to gather data from a large and representative sample, ensuring the statistical significance of our findings. By employing structured questionnaires and standardized data collection methods, we guarantee the reliability and validity of the information we present to our clients.
Quantitative research is particularly effective in measuring the prevalence of trends, assessing market size, and gauging the impact of various factors on consumer behavior. The numerical precision attained through this approach equips our clients with actionable insights, facilitating data-driven decision-making and strategy formulation.


Our Specialized Toolbox for Industry-Specific Market Research
We deploy a specialized arsenal of techniques tailored to meet your unique requirements. Here's a glimpse into our comprehensive toolbox:

Information Procurement
The stage entails acquiring market data or relevant information through various sources and methodologies.


Market Research Approach
We utilize both top-down and bottom-up approaches in market research analysis to achieve a comprehensive understanding of the market dynamics, leveraging the broad perspective of industry trends and macroeconomic factors alongside detailed insights from specific segments and individual companies.

Porters Five Forces Analysis
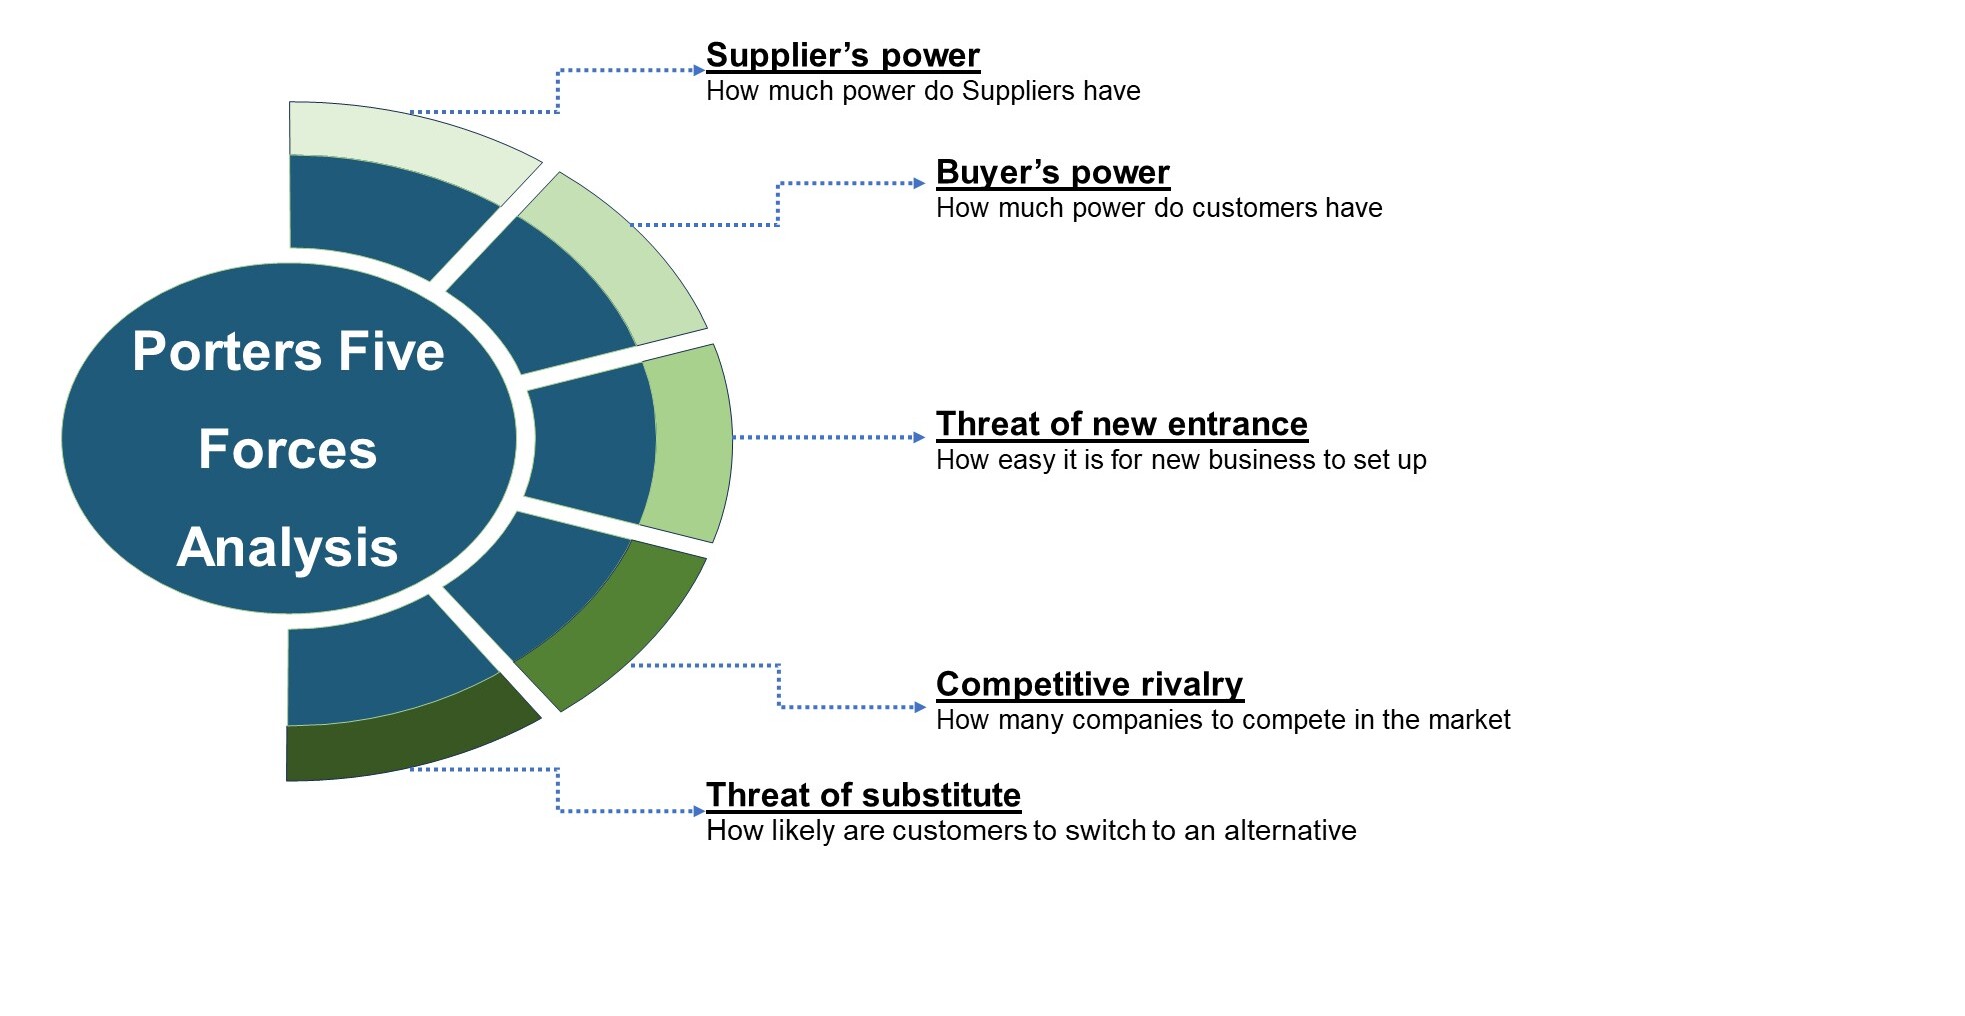
We conduct Porter's Five Forces analysis to evaluate the competitive landscape of an industry, providing us with insights into factors that affect profitability and strategic positioning.
SWOT Analysis

Forecasting
We utilize a forecasting model to predict future consumption by considering parameters like population, economics, regulations, market competition, drivers, constraints, technology, and pricing. We also employ statistical techniques such as multilinear regression, exponential smoothing, moving average, ARIMA, and Monte Carlo simulations for accurate predictions. In econometric forecasting, we analyzed short-term and long-term event impacts, attributing values based on regulatory frameworks, economic factors, and market events.




 Speak to Our Analyst